Web security verification · Reports ready to hand over
The security evidence your client is about to ask you for
We assess your websites, web apps and domains and hand you a documented record: what was tested, what we found, what to fix and in what order. A technical report for the people who touch the code, a one-page summary for the people who sign, and a signed letter of attestation ready to hand to clients, auditors and procurement.
OWASP WSTG
NIST SP 800-115
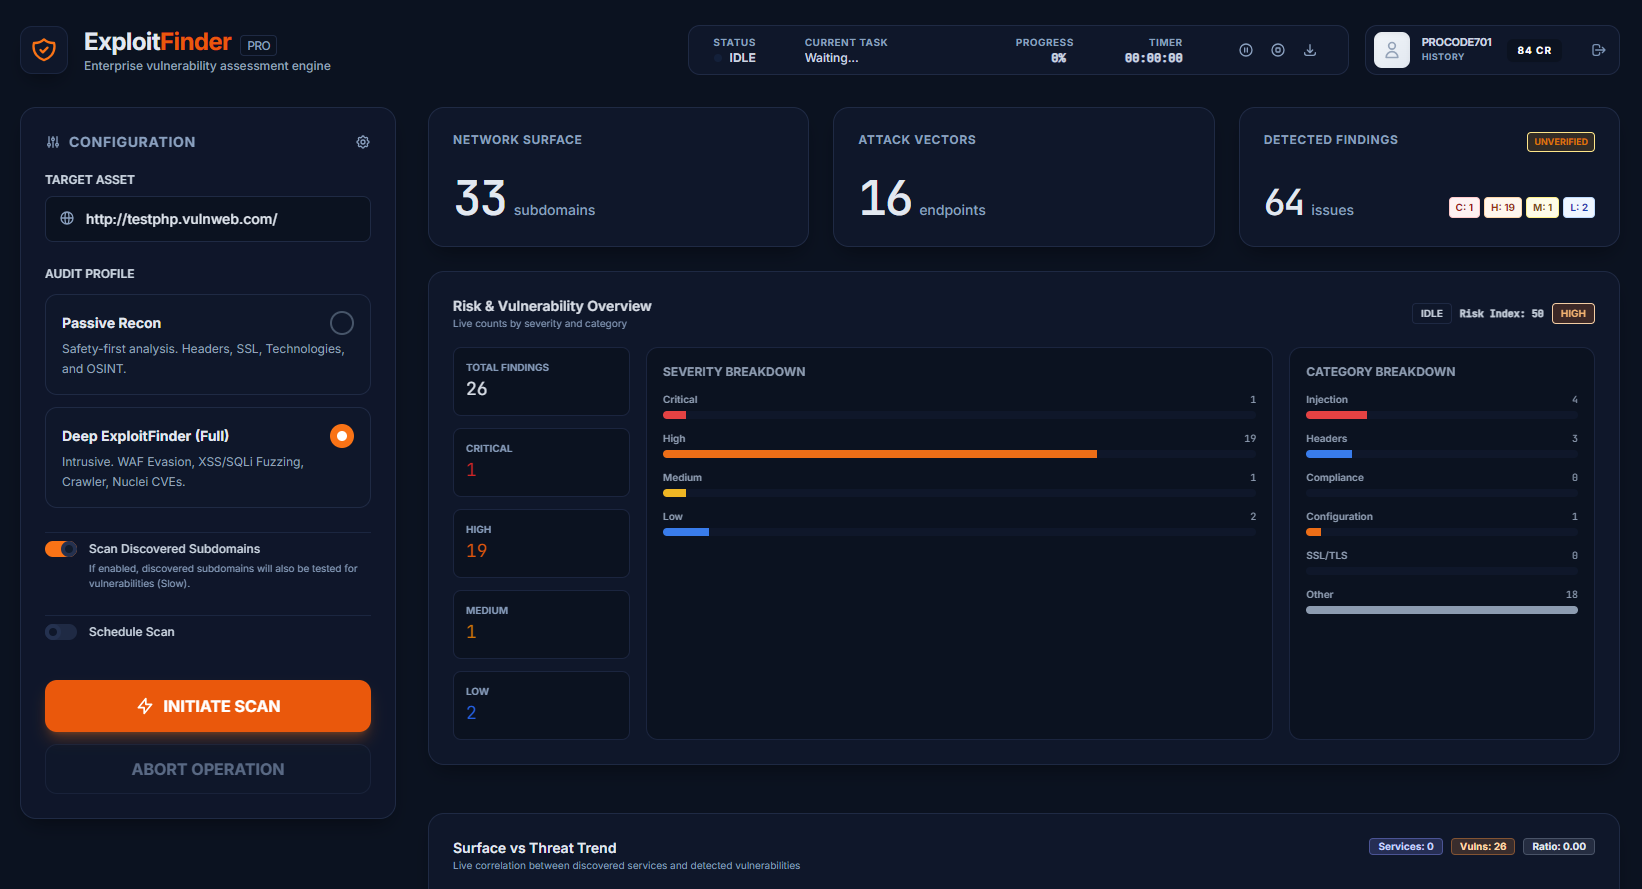
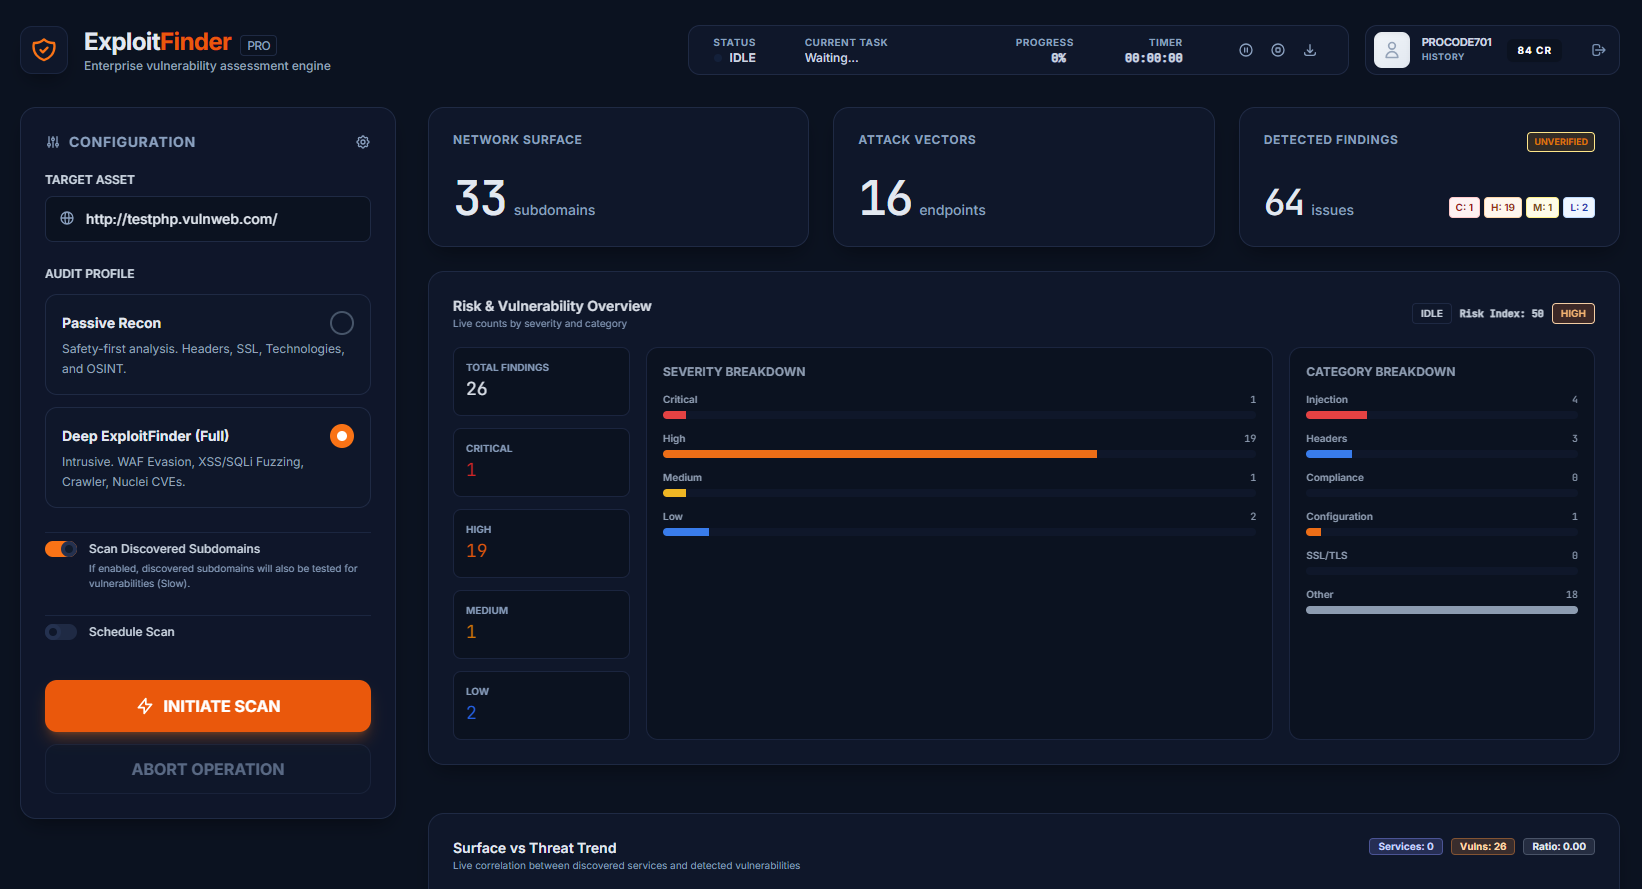
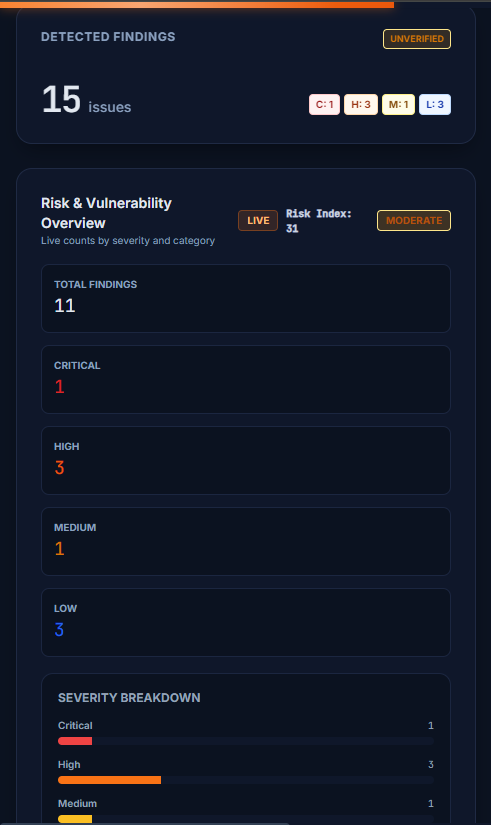
On the plans with manual validation, every finding is checked by a person before it reaches the report: false positives are filtered out, not merely flagged by an engine.
You are here for a specific reason
This is not technical curiosity. It is that someone, outside this page, is asking you for proof.
The client who wants guarantees
Before signing, they want to know how you handle their data. And they want to see something, not hear that "you're careful".
The tender or the specification
A documented security verification sits in the requirements. Without that document, the bid does not pass.
Your client's questionnaire
NIS2, GDPR Art. 32, supply-chain security: it landed in your inbox and it is waiting for an answer.
The deadline moving closer
You have weeks, not months. And you cannot hand over something that falls apart at the first question.
You don't need another scanner.
You need a document that holds up in a room where you are not the one answering.
The report you hand to your client
A real document, not an automatic log. It says what was tested, what was found, what it means for the business, and what to fix first, and it carries a signature.
CONFIDENTIAL
Executive summary
Residual risk
Low (post-remediation)
Signed attestationVerified and delivered with the report
-
Human-Readable Executive Summary
Business language for the board, understandable without technical jargon.
-
Technical Deep-Dive
Technical details, Proof of Concept, and reproduction steps for developers.
-
Remediation Roadmap
Not just "what's wrong," but "how to fix it" with time priority.
-
Compliance ready
Mapping of the findings onto ISO/IEC 27001 and GDPR standards.
Sample generated on a public test environment, with anonymised data.
What you walk away with, not just what we scan
The core of our scanner includes the best OWASP ZAP signatures, enhanced by business logic analysis. We offer a complete, validated, and historicized Online Vulnerability Scan.
OWASP ZAP Engine
Deep integration with OWASP ZAP to detect SQLi, XSS, and misconfigurations with industry-standard precision.
Asset Discovery
Subdomain enumeration, directory mapping, and exposed JavaScript asset analysis.
Service Exposure Analysis
Service enumeration and component fingerprinting with vulnerability correlation.
Validation Engine
Verification workflow to reduce false positives and qualify real impact.
Repetition on a schedule
The same verification run again when you need it, with the comparison between one cycle and the previous one.
Vulnerability Prioritization
Ranking findings by technical risk, exploitability, and business impact.
Human + Technical Report
Readable document for stakeholders and technical detail for the operational team.
AutoFix Readiness
Remediation guidance ready for structured patching and hardening workflows.
Decision Layer
Risk synthesis, priority, and remediation roadmap with supporting evidence.
Repeatable analysis framework
Each report cycle follows a stable 6-phase pipeline, designed to reduce noise, increase confidence, and accelerate remediation decisions.
1. Perimeter Discovery
We map domains, endpoints, and application surfaces to define the real perimeter.
- Enumeration of publicly reachable hosts and services.
- JavaScript analysis and dynamic endpoint mapping.
- Perimeter reconfirmed at every cycle, before the verification is run again.
2. Exposed Service Analysis
We classify stacks and components to find exposures and relevant vulnerabilities.
- Fingerprinting of at-risk technologies and versions.
- Vulnerability-component-impact correlation.
- Evaluation of exploitability and priority.
3. Attack Surface Mapping
We cover classic applications and SPAs with a state-aware approach for hidden endpoints.
- Dynamic flows, forms, application states, and private areas.
- DOM-driven scanning for modern applications.
- Fallback crawler for legacy compatibility coverage.
4. DAST and Active Verification
We stress application controls with dynamic testing and targeted detection.
- Runtime analysis of input handling and security controls.
- Detection of known exposures and common misconfigurations.
5. Controlled Injection Modules
We responsibly simulate critical vectors to validate real technical impact.
- SQLi tests, contextual XSS, and command injection where applicable.
- Manual confirmation of high-severity cases.
- Reproducible evidence for effective remediation.
6. Risk Scoring and Decision Reporting
We convert technical data into operational priorities and roadmaps with clear ownership.
- Risk rating with business context and urgency.
- Executive conclusion for non-technical stakeholders.
- Concrete remediation plan, not just a list of findings.
Engines used and orchestrated internally, automatically activated by AI based on scan context
RECONNAISSANCE
S
Subfinder
Asset & subdomain discovery
A
Amass
OSINT & DNS enumeration
Sh
Shodan
Internet-wide host search
Th
theHarvester
Email & people OSINT
PORT & SERVICE SCAN
CORE
N
Nmap
Port scanner & fingerprint
M
Masscan
Ultra-fast port scan
Rk
RustScan
Fastest port scanner
Ns
Nikto
Web server misconfig scan
WEB APPLICATION
CORE
Z
OWASP ZAP
Active web app scanner
CORE
F
FFUF
Directory & param fuzzer
Gf
Gobuster
URI & DNS bruteforce
Nu
Nuclei
Template-based vuln scan
VULNERABILITY EXPLOITATION
CORE
Sq
SQLMap
SQL injection automation
CORE
Xs
XSStrike
XSS detection & exploit
CORE
Cm
Commix
Command injection tester
Mf
Metasploit
Exploit framework
NETWORK & TRAFFIC
Ws
Wireshark
Packet capture & analysis
Hx
Hydra
Network brute-force
Md
Medusa
Parallel login bruteforce
Nc
Netcat
Raw TCP/UDP tool
CORRELATION & AI · PROPRIETARY
AI
EF
ExploitFinder Correlator
Cross-tool finding correlation & risk scoring
AI
DA
Deep Audit Engine
Autonomous pentest orchestration & reporting
One verification, three perimeters
The verification is always the same: external, manually validated, with a signed letter of attestation. Only the perimeter it covers changes. If you need the evidence to stay valid, we repeat it on a schedule.
The verification
Single perimeter
€490 one-off
For when you have to hand a client, a tender specification or an enterprise customer evidence that stands up on its own.
- Signed letter of attestation
- 1 primary domain and its subdomains
- Manual validation of findings
- Executive + technical report
- Free 30-day retest
- Delivered in 5 working days
Not sure your case fits here? First we read the perimeter.
More domains
On quotation one-off
Based on the number of domains you declare
For groups, agencies and software houses that have to cover several sites under one single piece of evidence.
- One single report covering every domain
- Same manual validation standard
- One attestation listing the domains
- Separate sub-report for each domain
Enterprise and NIS2
from €4,900 one-off
Extended perimeter, NDA and a dedicated contact
For critical infrastructures and for anyone who has to answer an NIS2 requirement or an auditor.
- Evidence laid out for the auditor
- Perimeter agreed in writing
- Single point of contact and NDA
- Extended retest window
Do you need the evidence to stay valid over time?
We repeat the same verification every 4 or 6 months, with the comparison between one cycle and the previous one. Dedicated terms from 3 cycles.
- Only on domains you own, with written authorization
- Prices exclude VAT and applicable taxes
From snapshot to governance
A single verification ages, and an automatic scan only delivers noise. We work in cycles: same verification, same standard, comparison between one cycle and the previous one.
Traditional Approach
Spot Analysis
Static output limited to execution time. No risk historicization or strategic decision support for remediation.
Exploit Finder Pro
Scheduled Verification
The same verification run again on a schedule, with the comparison between one cycle and the previous one and guided prioritisation of the interventions.
Exploit Finder Enterprise
Extended Perimeter and NIS2
For critical infrastructures and regulatory requirements: perimeter agreed in writing, evidence laid out for the auditor, a single point of contact.
- Noise reduction: validation and contextualization of findings.
- Faster time-to-decision: decision-makers understand immediately what to do.
- Continuity: the verification is repeated over time, it does not stay a one-off snapshot.
- Remediation roadmap: ownership, priority and follow-up over time.
Methodologies and Techniques Used
Assessment methodology aligned with recognized frameworks: reconnaissance, fingerprinting, misconfiguration review, vulnerability validation, and remediation guidance.
Demonstrate Your Capabilities To Clients, Regulators And Investors.
Compliance ReportingAcross the world, we all have different ways to demonstrate our cyber security strategy. For many businesses using a good governance framework is a great way to demonstrate to clients, regulators and investors how seriously you take IT Governance.
Exploit Finder has a compliance engine built into the platform allowing you to export evidence data for a wide range of IT Governance Frameworks including but not limited to:
- Cyber Essentials (UK)
- Essential 8 (Australia)
- NIST (USA)
- SOC 2 (Worldwide)
- ISO 27001 (Worldwide)
- HIPAA (USA)
Not sure your case fits? We read the perimeter.
Twenty-four hours, only on what your domain already exposes publicly: no authorization to sign, no access to your systems, no report. We tell you in writing whether the €490 verification is what you need, on which perimeter, and what we would look at.
Read the perimeter